Zero trust is a security model that trusts no user or device by default and verifies every access request by identity and context. Instead of assuming anything inside the network is safe, each request is authenticated, authorized and continuously checked. It matters because the old perimeter has dissolved: people, devices and applications now sit everywhere. The practical starting point is strong identity and your most critical assets.
What is zero-trust security?
Zero trust is a security approach built on one idea: no user, device or request is trusted automatically, wherever it comes from. Every access attempt must prove who it is and that it is allowed, every time. It replaces the old model of a hard network perimeter with a soft, trusted interior, which attackers routinely bypass once they are inside.
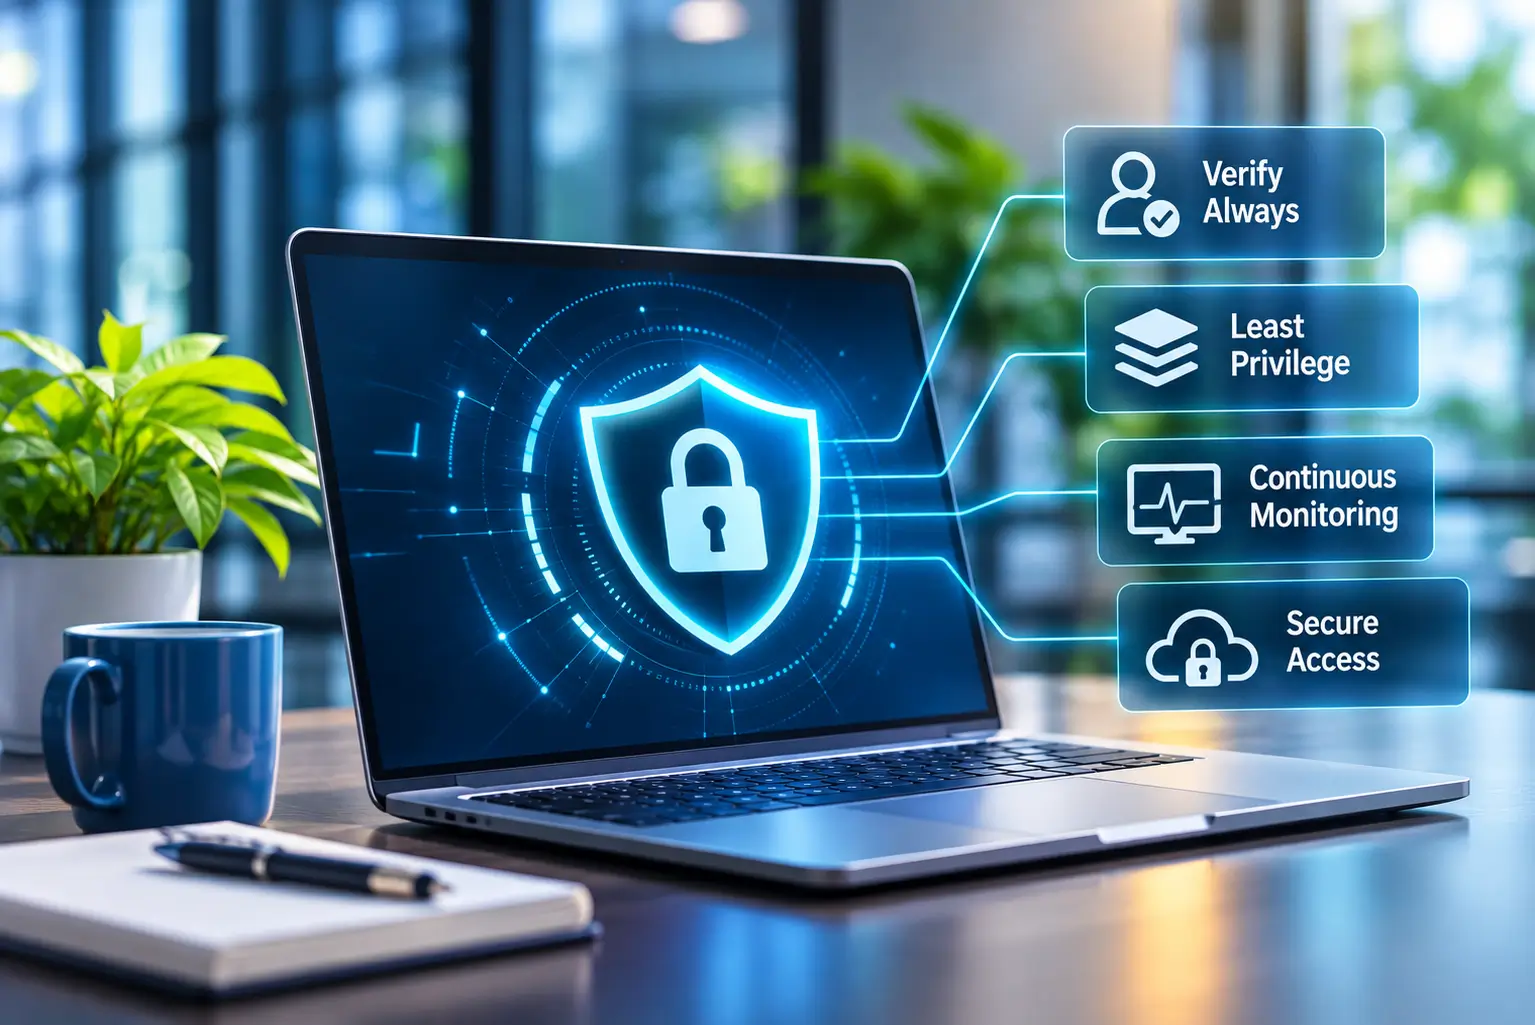
Three principles define it. Verify explicitly: authenticate and authorize every request using identity, device health and context. Use least privilege: give each identity only the access it needs, for only as long as it needs it. Assume breach: design as if attackers are already inside, so you contain damage with segmentation and monitoring.
Why zero trust now?
The network perimeter has effectively disappeared. People work from anywhere, applications live in multiple clouds, and devices range from managed laptops to personal phones. A firewall around the office no longer protects much of what matters. At the same time, ransomware and credential theft thrive on flat, over-trusted networks where one compromised account can reach everything.
Zero trust addresses both shifts. By verifying every request and limiting what any identity can reach, it shrinks the blast radius of a breach and removes the implicit trust attackers depend on.
The pillars of a zero-trust architecture
Zero trust applies across several domains. Strong programs address each one.
| Pillar | What it covers | Example controls |
|---|---|---|
| Identity | Who is requesting access | MFA, conditional access, least privilege |
| Devices | The health of the endpoint | Device compliance, EDR, patch status |
| Network | How traffic moves | Microsegmentation, no flat networks |
| Applications | Access to apps and workloads | Per-app authorization, no implicit trust |
| Data | Protecting the information itself | Classification, encryption, access governance |
Where to start: a practical path
You do not implement zero trust all at once. Start where it delivers the most risk reduction fastest.
- Identity first. Enforce multi-factor authentication, conditional access and least privilege. This is the single highest-impact step. See identity and access management.
- Protect your critical assets. Identify the data and systems that matter most and tighten access and monitoring around them, including information protection and governance.
- Verify devices. Require healthy, compliant devices before granting access.
- Segment and monitor. Break up flat networks and watch for anomalies continuously.
- Extend to cloud. Apply the same principles to cloud workloads with cloud security.
Start here
If you do one thing first, make it identity: MFA, conditional access and least privilege close the door most attackers walk through.
Common misconceptions
Zero trust is not a product you install, and no single vendor delivers all of it. It is an architecture you build from identity, device, network, application and data controls over time. It is also more than replacing a VPN: swapping remote-access tools helps, but true zero trust changes how every request is trusted, not just how people connect from home. Our zero-trust services treat it as a program, not a purchase.
How Billow helps
Billow designs and implements zero-trust architecture for US enterprises and public agencies, starting with identity and extending across devices, data and cloud, with detection and response through SIEM and SOAR. If you want a practical, phased path to zero trust, our cybersecurity team can help you prioritize.
Frequently asked questions
What does zero trust mean in simple terms?
It means never trust, always verify. No user or device is trusted just because it is on your network. Every request to access a system or data must prove its identity and that it is authorized, every time, and is granted the least access needed.
Is zero trust a product I can buy?
No. Zero trust is a security strategy and architecture, not a single product. You build it from identity, device, network, application and data controls, often using several tools, and roll it out in phases rather than all at once.
Where should I start with zero trust?
Start with identity. Enforce multi-factor authentication, conditional access and least-privilege access, then protect your most critical data and systems. Identity controls deliver the biggest risk reduction for the least effort, because stolen credentials are behind most breaches.
Does zero trust replace the VPN?
It can change how remote access works, often replacing broad VPN access with per-application, identity-verified access. But zero trust is broader than VPN replacement: it governs trust for every request, not only connections from outside the office.
How long does zero trust take to implement?
It is an ongoing journey rather than a project with an end date. Most organizations see meaningful risk reduction within the first phases, identity and critical-asset protection, in a few months, then extend segmentation, device and cloud controls over time.
